Google Raises Cloud Security Bounties to $250,000 to Catch Root-Level Vulnerabilities
'/> </pattern> </defs> <rect width='1200' height='675' fill='url(%23g)'/> <rect width='1200' height='675' fill='url(%23dots)'/> <rect x='60' y='210' width='6' height='80' fill='%23f5a524'/> <text x='90' y='268' font-size='15' font-weight='900' letter-spacing='5' fill='%23f5a524'>NEWSEZE</text> <g font-family='Inter, Arial, sans-serif'> <text x='60' y='320' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Google Raises Cloud Security Bounties</text><text x='60' y='376' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>to $250,000 to Catch Root-Level</text><text x='60' y='432' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Vulnerabilities…</text> <text x='60' y='620' font-size='14' font-weight='700' letter-spacing='3' fill='rgba(255,255,255,0.7)'>SECURITYWEEK VIA GOOGLE NEWS · NEWSEZE</text> </g> </svg>)
As cloud infrastructure becomes critical to business and government operations, Google's expanded bounty signals the industry's struggle to find and fix the most damaging security flaws before adversaries exploit them.
Sourcing & attribution. Newseze provides AI-curated summaries, narrative framing, and editorial analysis. The underlying reporting was contributed by SecurityWeek via Google News; tap “Open original source” above to read their full reporting and support the contributing newsroom directly.
Newseze's algorithm reads the story and answers your question — calmly, factually, with source attribution. No comments, no flame wars — just answers.
No questions yet. Be the first.
Answers reflect Newseze's editorial framework applied under fair use (17 U.S.C. § 107). Not financial, legal, medical, or tax advice. Hate speech and racial slurs are blocked.
Related stories

Why it mattersTwo critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week. Langflow is an open-source tool for building AI agents and workflows, and&n…
Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week. Langflow is an …
 By Chella·13h ago

Why it mattersSome attacks this week didn't need much of a trick. A fake support call, a trusted extension, a shared link, or a device with no password.
Some attacks this week didn't need much of a trick. A fake support call, a trusted extension, a shared link, or a device with no password. Small things that peo…
By Chella·8h ago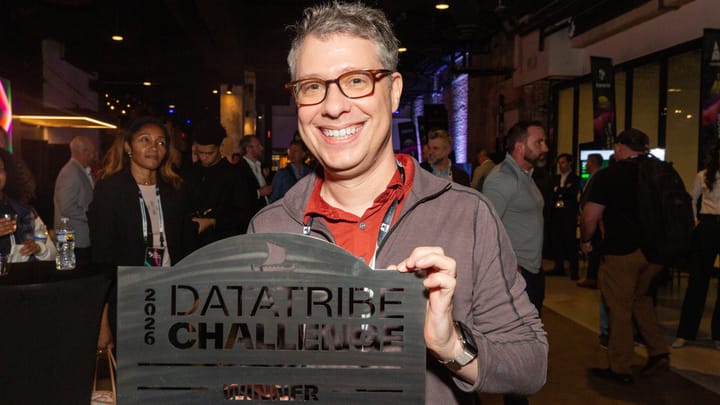
Why it mattersThe cybersecurity market is difficult to predict, but a glimpse into the annual DataTribe Challenge shows what's trending and what's not.
By Chella·3d ago'/> </pattern> </defs> <rect width='1200' height='675' fill='url(%23g)'/> <rect width='1200' height='675' fill='url(%23dots)'/> <rect x='60' y='210' width='6' height='80' fill='%23f5a524'/> <text x='90' y='268' font-size='15' font-weight='900' letter-spacing='5' fill='%23f5a524'>NEWSEZE</text> <g font-family='Inter, Arial, sans-serif'> <text x='60' y='320' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Critical PHP vulnerabilities raise</text><text x='60' y='376' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>worldwide concerns as government</text><text x='60' y='432' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>websites go offline, researchers…</text> <text x='60' y='620' font-size='14' font-weight='700' letter-spacing='3' fill='rgba(255,255,255,0.7)'>US-CERT VIA GOOGLE NEWS · NEWSEZE</text> </g> </svg>)
Why it mattersCritical PHP vulnerabilities raise worldwide concerns as government websites go offline, researchers report AI-assisted attacks Industrial Cyber
By Chella·Oct 26