BambooToken malware controls Windows and Linux systems via MQTT - BleepingComputer
'/> </pattern> </defs> <rect width='1200' height='675' fill='url(%23g)'/> <rect width='1200' height='675' fill='url(%23dots)'/> <rect x='60' y='210' width='6' height='80' fill='%23f5a524'/> <text x='90' y='268' font-size='15' font-weight='900' letter-spacing='5' fill='%23f5a524'>NEWSEZE</text> <g font-family='Inter, Arial, sans-serif'> <text x='60' y='320' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>BambooToken malware controls Windows</text><text x='60' y='376' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>and Linux systems via MQTT -</text><text x='60' y='432' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>BleepingComputer…</text> <text x='60' y='620' font-size='14' font-weight='700' letter-spacing='3' fill='rgba(255,255,255,0.7)'>BLEEPINGCOMPUTER VIA GOOGLE · NEWSEZE</text> </g> </svg>)
BambooToken malware controls Windows and Linux systems via MQTT BleepingComputer
Sourcing & attribution. Newseze provides AI-curated summaries, narrative framing, and editorial analysis. The underlying reporting was contributed by BleepingComputer via Google News; tap “Open original source” above to read their full reporting and support the contributing newsroom directly.
Newseze's algorithm reads the story and answers your question — calmly, factually, with source attribution. No comments, no flame wars — just answers.
No questions yet. Be the first.
Answers reflect Newseze's editorial framework applied under fair use (17 U.S.C. § 107). Not financial, legal, medical, or tax advice. Hate speech and racial slurs are blocked.
Related stories

Why it mattersCybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334.
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Secur…
 By Chella·1h ago

Why it mattersA Chinese threat actor has been attributed to a spear-phishing campaign that exploits recently patched security flaws in Google Chrome and Microsoft Windows to deliver a malicious JavaScript backdoor called GRIMWEDGE. Vo…
A Chinese threat actor has been attributed to a spear-phishing campaign that exploits recently patched security flaws in Google Chrome and Microsoft Windows to …
By Chella·14h ago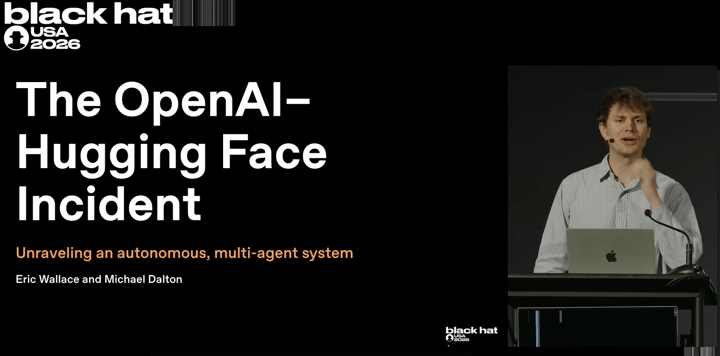
Why it mattersThe 'Breaking' News: The OpenAI–Hugging Face Incident - A Technical Reconstruction and Its Implications for AI At this Black Hat USA 2026 talk, OpenAI security engineers and researchers will reconstruct the OpenAI-Huggin…
The 'Breaking' News: The OpenAI–Hugging Face Incident - A Technical Reconstruction and Its Implications for AI At this Black Hat USA 2026 talk, OpenAI security …
By Chella·41m ago'/> </pattern> </defs> <rect width='1200' height='675' fill='url(%23g)'/> <rect width='1200' height='675' fill='url(%23dots)'/> <rect x='60' y='210' width='6' height='80' fill='%23f5a524'/> <text x='90' y='268' font-size='15' font-weight='900' letter-spacing='5' fill='%23f5a524'>NEWSEZE</text> <g font-family='Inter, Arial, sans-serif'> <text x='60' y='320' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>CISA Flags New Active Exploit</text><text x='60' y='376' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Vulnerability for Federal Agency</text><text x='60' y='432' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Review…</text> <text x='60' y='620' font-size='14' font-weight='700' letter-spacing='3' fill='rgba(255,255,255,0.7)'>CISA ALERTS VIA GOOGLE NEWS · NEWSEZE</text> </g> </svg>)
Why it mattersGovernment and private-sector IT teams now have official notice of a vulnerability actively being exploited in the wild, requiring immediate patch assessment and deployment priority.
CISA Adds One Known Exploited Vulnerability to Catalog CISA (.gov)
By Chella·1d ago