As Russia's Cyberwar Evolves, Belarus Steps Forward
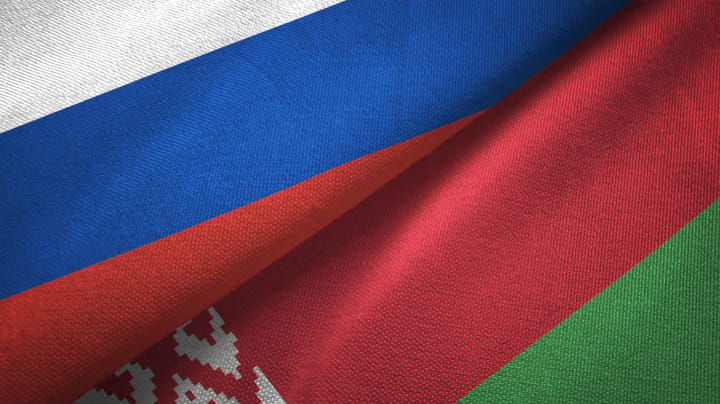
The "FrostyNeighbor" advanced persistent threat (APT) launched a destructive attack in Ukraine and is raising concerns about deeper alignment with Russian cyber objectives.
Sourcing & attribution. Newseze provides AI-curated summaries, narrative framing, and editorial analysis. The underlying reporting was contributed by Dark Reading; tap “Open original source” above to read their full reporting and support the contributing newsroom directly.
Newseze's algorithm reads the story and answers your question — calmly, factually, with source attribution. No comments, no flame wars — just answers.
No questions yet. Be the first.
Answers reflect Newseze's editorial framework applied under fair use (17 U.S.C. § 107). Not financial, legal, medical, or tax advice. Hate speech and racial slurs are blocked.
Related stories

Why it mattersThe U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added two security flaws impacting Cisco and GitLab software to its Known Exploited Vulnerabilities (KEV), citing evidence of active exploitati…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added two security flaws impacting Cisco and GitLab software to its Known Exploited…
 By Chella·1h ago

Why it mattersDrupal has warned that threat actors are exploiting a "highly critical" security flaw in its Commerce Core component. The vulnerability, tracked as CVE-2026-118539 (CVSS score: N/A), is a case of missing authorization af…
Drupal has warned that threat actors are exploiting a "highly critical" security flaw in its Commerce Core component. The vulnerability, tracked as CVE-2026-118…
By Chella·1h ago
Why it mattersThreat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba. The…
Threat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Clau…
By Chella·17h ago
Why it mattersThe U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a security flaw impacting Broadcom VMware ESX to its Known Exploited Vulnerabilities (KEV) catalog, after CrowdStrike revealed that it h…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a security flaw impacting Broadcom VMware ESX to its Known Exploited Vulnera…
By Chella·1d ago