Cisco Zero-Day Highlights API Endpoint Authentication Issues
The authentication bypass flaw CVE-2026-76460 impacts Cisco's Identity Services Engine (ISE) and received a maximum 10 out of 10 CVSS score.
Sourcing & attribution. Newseze provides AI-curated summaries, narrative framing, and editorial analysis. The underlying reporting was contributed by Dark Reading; tap “Open original source” above to read their full reporting and support the contributing newsroom directly.
Newseze's algorithm reads the story and answers your question — calmly, factually, with source attribution. No comments, no flame wars — just answers.
No questions yet. Be the first.
Answers reflect Newseze's editorial framework applied under fair use (17 U.S.C. § 107). Not financial, legal, medical, or tax advice. Hate speech and racial slurs are blocked.
Related stories
Why it mattersThe new program expands Vectra AI's partner strategy as increasingly complex security environments and the growing use of AI create demand for broader AI expertise, services, and security outcomes.
 By Chella·1h ago
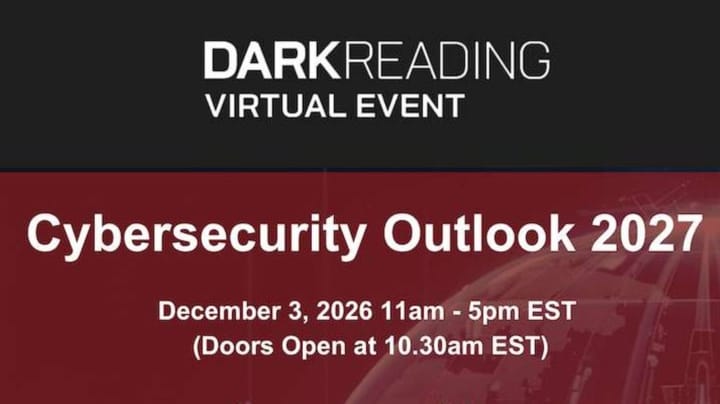
Why it matters[Virtual Event] Cybersecurity Outlook 2027
By Chella·just now
Why it mattersWordPress today released patches to fix a new set of vulnerabilities in its core software, one of which could allow a crafted web link, opened by a logged-in administrator, to install a theme from the official WordPress.…
WordPress today released patches to fix a new set of vulnerabilities in its core software, one of which could allow a crafted web link, opened by a logged-in ad…
By Chella·5h ago
Why it mattersThe Iran-linked "hacktivist" persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a Delphi-based utility known as CRUDEEXCLUDE. "HEAVYGRAM offers builtin comman…
The Iran-linked "hacktivist" persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a Delphi-based uti…
By Chella·1d ago