Researchers Infiltrate Microsoft Tech Support Scam Operation
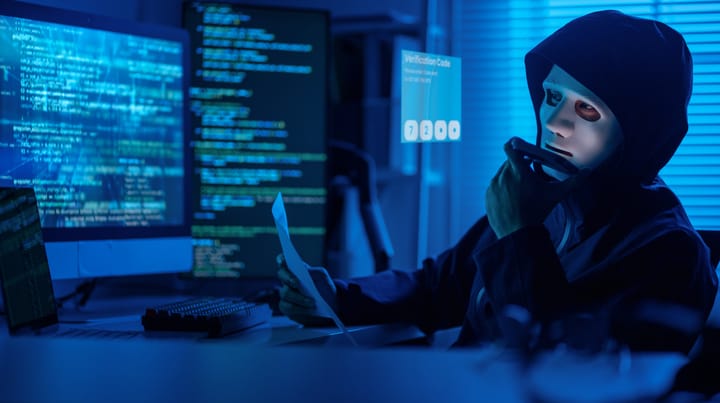
A large-scale scam operation impersonating Microsoft uses a malicious traffic distribution system (TDS) run by a Russian organization and abuses thousands of Cloudflare links.
Sourcing & attribution. Newseze provides AI-curated summaries, narrative framing, and editorial analysis. The underlying reporting was contributed by Dark Reading; tap “Open original source” above to read their full reporting and support the contributing newsroom directly.
Newseze's algorithm reads the story and answers your question — calmly, factually, with source attribution. No comments, no flame wars — just answers.
No questions yet. Be the first.
Answers reflect Newseze's editorial framework applied under fair use (17 U.S.C. § 107). Not financial, legal, medical, or tax advice. Hate speech and racial slurs are blocked.
Related stories
'/> </pattern> </defs> <rect width='1200' height='675' fill='url(%23g)'/> <rect width='1200' height='675' fill='url(%23dots)'/> <rect x='60' y='210' width='6' height='80' fill='%23f5a524'/> <text x='90' y='268' font-size='15' font-weight='900' letter-spacing='5' fill='%23f5a524'>NEWSEZE</text> <g font-family='Inter, Arial, sans-serif'> <text x='60' y='320' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Feds Suspect Ransom Negotiator Ran</text><text x='60' y='376' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>ShinyHunters Extortion Site</text> <text x='60' y='620' font-size='14' font-weight='700' letter-spacing='3' fill='rgba(255,255,255,0.7)'>KREBS ON SECURITY · NEWSEZE</text> </g> </svg>)
Why it mattersU.S. federal investigators pursuing the ShinyHunters hacking group that recently stole highly sensitive data from the FBI have identified executives at two different ransomware negotiation firms who maintained unusually …
U.S. federal investigators pursuing the ShinyHunters hacking group that recently stole highly sensitive data from the FBI have identified executives at two diff…
 By Chella·9h ago
'/> </pattern> </defs> <rect width='1200' height='675' fill='url(%23g)'/> <rect width='1200' height='675' fill='url(%23dots)'/> <rect x='60' y='210' width='6' height='80' fill='%23f5a524'/> <text x='90' y='268' font-size='15' font-weight='900' letter-spacing='5' fill='%23f5a524'>NEWSEZE</text> <g font-family='Inter, Arial, sans-serif'> <text x='60' y='320' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Microsoft fixes game, app crashes</text><text x='60' y='376' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>caused by recent Windows update -</text><text x='60' y='432' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>BleepingComputer…</text> <text x='60' y='620' font-size='14' font-weight='700' letter-spacing='3' fill='rgba(255,255,255,0.7)'>BLEEPINGCOMPUTER VIA GOOGLE · NEWSEZE</text> </g> </svg>)
Why it mattersMicrosoft fixes game, app crashes caused by recent Windows update BleepingComputer
By Chella·8h ago'/> </pattern> </defs> <rect width='1200' height='675' fill='url(%23g)'/> <rect width='1200' height='675' fill='url(%23dots)'/> <rect x='60' y='210' width='6' height='80' fill='%23f5a524'/> <text x='90' y='268' font-size='15' font-weight='900' letter-spacing='5' fill='%23f5a524'>NEWSEZE</text> <g font-family='Inter, Arial, sans-serif'> <text x='60' y='320' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Inside the Underground Market for Know</text><text x='60' y='376' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Your Client Services -</text><text x='60' y='432' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>BleepingComputer…</text> <text x='60' y='620' font-size='14' font-weight='700' letter-spacing='3' fill='rgba(255,255,255,0.7)'>BLEEPINGCOMPUTER VIA GOOGLE · NEWSEZE</text> </g> </svg>)
Why it mattersInside the Underground Market for Know Your Client Services BleepingComputer
By Chella·9h ago
Why it mattersIvanti, Cisco, and Palo Alto Networks all had vulnerabilities in edge devices come under fire this week. Now BeyondTrust joins the group.
By Chella·3d ago