UAE, Saudi Arabia Face Onslaught of Increasingly Complex Cyberattacks
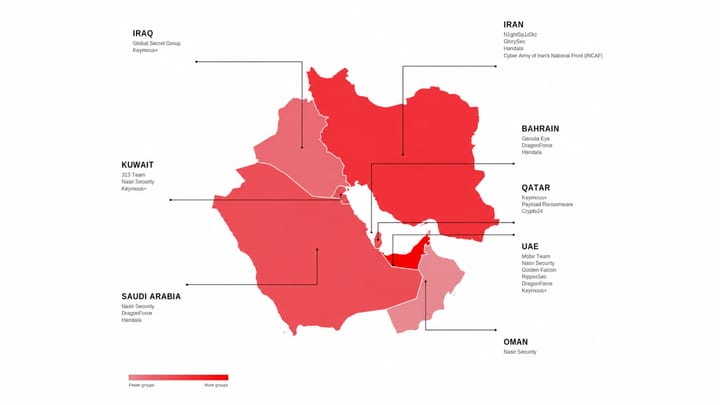
The United Arab Emirates and Kingdom of Saudi Arabia together absorbed 50% of all cyberattacks recorded across the Gulf region in the first half of 2026.
Sourcing & attribution. Newseze provides AI-curated summaries, narrative framing, and editorial analysis. The underlying reporting was contributed by Dark Reading; tap “Open original source” above to read their full reporting and support the contributing newsroom directly.
Newseze's algorithm reads the story and answers your question — calmly, factually, with source attribution. No comments, no flame wars — just answers.
No questions yet. Be the first.
Answers reflect Newseze's editorial framework applied under fair use (17 U.S.C. § 107). Not financial, legal, medical, or tax advice. Hate speech and racial slurs are blocked.
Related stories

Why it mattersA Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through fake websites. The attacks, detected on September 3 and 4, 2…
A Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through …
 By Chella·3h ago
Why it mattersThreat actors stole 170 private repositories using an OAuth token stolen from a former employee's computer through the TanStack npm supply chain attack.
By Chella·18h ago
Why it mattersThe maximum-severity vulnerability in Cisco ISE could allow attackers to bypass authentication on a widely deployed enterprise identity platform, making this a high-priority patch for organizations managing network acces…
The authentication bypass flaw CVE-2026-76460 impacts Cisco's Identity Services Engine (ISE) and received a maximum 10 out of 10 CVSS score.
By Chella·4d ago'/> </pattern> </defs> <rect width='1200' height='675' fill='url(%23g)'/> <rect width='1200' height='675' fill='url(%23dots)'/> <rect x='60' y='210' width='6' height='80' fill='%23f5a524'/> <text x='90' y='268' font-size='15' font-weight='900' letter-spacing='5' fill='%23f5a524'>NEWSEZE</text> <g font-family='Inter, Arial, sans-serif'> <text x='60' y='320' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Microsoft Patches Nearly 400</text><text x='60' y='376' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Vulnerabilities, Including Active</text><text x='60' y='432' font-size='44' font-weight='800' fill='rgba(255,255,255,0.97)' letter-spacing='-0.5'>Exploits…</text> <text x='60' y='620' font-size='14' font-weight='700' letter-spacing='3' fill='rgba(255,255,255,0.7)'>KREBS ON SECURITY · NEWSEZE</text> </g> </svg>)
Why it mattersMicrosoft's monthly security update addresses vulnerabilities already under active attack, making timely deployment critical for users to protect systems against ongoing threats.
Microsoft today released updates to remedy at least 398 security vulnerabilities in its Windows operating systems and supported software, including one weakness…
 By Marcus·Aug 11